Is Virtual Therapy Confidential? What to Know
How Virtual Therapy Confidentiality Works Under HIPAA
The short answer to the question of is virtual therapy confidential: yes, but the protection depends on the platform, the setting, and your therapist's rules. This guide explains what keeps sessions private, where the gaps are, and how to close them.
Virtual therapy confidentiality is the legal and ethical obligation of a licensed provider to protect everything discussed and recorded during a remote session. Under HIPAA telehealth guidance, that obligation applies whether you meet in an office or over video. The rule does not weaken because the session happens online. What changes is who else can access the room.
What HIPAA Requires of Telehealth Platforms
HIPAA requires any platform handling protected health information (PHI) to use encryption in transit and at rest, enforce access controls, and sign a Business Associate Agreement with the provider. A general video tool without that agreement is not covered by HIPAA, and your session has no legal protection on that end.
Here is what each requirement means when you are the one in front of the screen.
Encryption in transit means video and audio are scrambled while traveling between your device and the therapist's, so an intercepted stream shows noise, not conversation. Encryption at rest means recordings, transcripts, and chat logs are scrambled on the platform's servers, so a breach does not expose readable content.
Access controls are the login gates: unique accounts, multi-factor authentication, role-based permissions so a billing clerk cannot open your clinical notes, and audit logs recording who viewed what and when. A shared generic login across staff is not meaningful access control.
A Business Associate Agreement (BAA) is a contract the platform signs with the provider, extending HIPAA's reach to the vendor. Without a signed BAA, your session data on that vendor's servers is outside HIPAA's protection entirely. It is the single most important thing to verify, and the one patients almost never ask about.
How to Tell Whether Your Therapist's Platform Is Actually Covered
You do not need to read the BAA yourself, just confirm it exists. Ask your therapist directly, in writing if possible:
"Is the platform we use covered by a signed Business Associate Agreement?"
"Is this a HIPAA-compliant telehealth platform, or a general video tool?"
A provider who treats privacy as a clinical standard answers without hesitation. A vague "it's secure" or "everyone uses it" is not the same as "yes, there is a BAA." Push for the yes.
The Limits of HIPAA in a Virtual Setting
HIPAA governs the provider and the platform, not your living room. A sibling walking in, a partner overhearing, or a smart speaker recording are outside the regulation entirely, and that gap is where most real-world breaches happen.
HIPAA binds covered entities (your provider) and business associates (the platform, billing service, EHR vendor). It does not bind your roommate, Wi-Fi router, smart speaker, or the family iPad you borrowed. The compliance chain ends at your device, and everything past that point is yours to manage.
Key TakeawayA signed BAA and end-to-end encryption protect the pipe between you and your therapist. They do nothing about the person on the other side of your bedroom door. Confirm the BAA, then handle the room yourself.
Exceptions to Therapist-Client Confidentiality You Should Know
Confidentiality is strong but not absolute. Every licensed U.S. provider operates under mandatory reporting and safety exceptions, and these apply identically in virtual care.
The standard exceptions include:
Imminent danger to you or another identifiable person
Suspected abuse or neglect of a child, elderly person, or dependent adult
Court order or valid legal subpoena
Qualified professional consultation, where a provider seeks guidance without revealing your identity
A good therapist explains these limits before the first session, not after. If yours has not, ask. Informed consent is not a formality; it is part of the APA Ethics Code standard for ethical practice.
Key TakeawayConfidentiality protects what you say in session. It does not protect you from a roommate hearing it through a thin wall. Physical and digital privacy are separate jobs, and you own one of them.
How to Ensure Privacy During Online Therapy
Privacy during online therapy comes down to two environments: the room you sit in and the network you connect through. Both need attention before session one.
Securing Your Physical Space
Book a room with a door that closes and ideally locks. Use white noise or a fan near the door, schedule sessions when the house is quietest, and tell household members in advance. Headphones do more for privacy than almost any other step.
Securing Your Digital Space
Use your own device, never a shared family computer. Connect through your home network or a personal hotspot, not public Wi-Fi. Enable two-factor authentication, keep your device updated, and close apps that might access your microphone or camera.
Pro TipRun a five-minute test call with a friend before your first session. It surfaces audio bleed, background noise, and camera angles while you still have time to fix them.
The Risks of Shared Devices, Public Wi-Fi, and Standard Video Tools
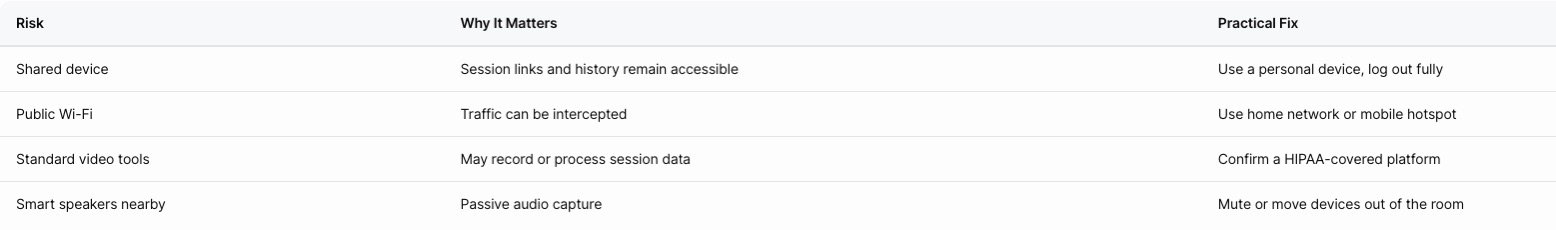
Three common setups quietly undermine confidentiality: a shared laptop, a coffee shop network, and a consumer video app with no healthcare agreement. Here is how each one leaks, plus a checklist to test your own setup.
How Shared Devices Leak Session Data
The leak is rarely dramatic. It is the browser autofilling your therapy portal password while a family member types in the same address bar, the session link in the "recently visited" list, an intake PDF in the shared Downloads folder, or a calendar event with your therapist's name syncing to a family calendar.
A shared device is not automatically disqualifying, but it requires cleanup most people skip. If you must use one, open a private window, decline the "save password" prompt, and log out rather than closing the tab. Better: use a personal device you alone unlock.
Why Public Wi-Fi Is Riskier Than It Looks
On an open network, anyone with basic tools can attempt to observe traffic. If the platform enforces end-to-end encryption, intercepted data is unreadable and the risk is largely neutralized; if not, session content is exposed.
The practical rule: never take a session on public Wi-Fi unless you have confirmed end-to-end encryption. If unsure, use your phone's personal hotspot, slower and data-hungry, but yours alone. A VPN supplements platform encryption on untrusted networks; it does not replace it.
What "End-to-End Encryption" Actually Looks Like
End-to-end encryption means content is scrambled on your device and unscrambled only on your therapist's device. The platform's own servers cannot read it, even in theory.
For a patient, the practical signals are:
A Five-Minute Privacy Check Before Your Session
Pro TipRun a five-minute test call with a friend before your first session. It surfaces audio bleed, background noise, and camera angles while you still have time to fix them, and it lets you confirm the platform's waiting room and mute controls actually work.
Standard Video Tools: The Quietest Risk
Is Virtual Therapy as Confidential as In-Person Sessions?
Protecting Privacy for Minors and Dependents in Virtual Care
Watch OutDo not eavesdrop on a teen's session, even with good intentions. If your child discovers you listened, the therapeutic alliance usually does not recover, and the sessions stop being useful.
Post-Session Data Management: What Happens After You Log Off
Ask your provider three questions:
Frequently Asked Questions
What are the legal standards for virtual therapy privacy under HIPAA?
HIPAA requires covered entities, including therapists and telehealth platforms, to protect protected health information (PHI) through administrative, physical, and technical safeguards. For virtual therapy confidentiality, this means using HIPAA-compliant video platforms with end-to-end encryption, obtaining informed consent, and having business associate agreements with any third-party vendors. Therapists must also conduct risk assessments and maintain secure session logs. These rules apply whether care is delivered in person or through virtual care.
Are there exceptions to confidentiality in virtual mental health sessions?
Yes. The exceptions to therapist-client confidentiality are the same online as in person. Therapists must report suspected child or elder abuse, respond to a court order, and take steps to prevent serious harm to you or someone else. In virtual sessions, your therapist should explain these limits during informed consent before your first appointment. If you have questions about what stays private, ask your licensed provider directly.
How can I ensure my home environment is private during a virtual therapy session?
Choose a room with a door you can close and use headphones to keep the conversation contained. Schedule sessions when others are away or occupied, and consider a white-noise machine near the door. Turn off smart speakers and other always-listening devices. Test your camera background before the session to make sure nothing personal is visible. If privacy at home is not possible, ask your therapist about options like a parked car or a private room at a library.
Does using a standard video conferencing tool compromise my therapy privacy?
It can. Platforms not designed for healthcare may lack end-to-end encryption, record metadata, or store data in ways that do not meet HIPAA compliance for telehealth. A licensed provider should use a HIPAA-compliant platform with a signed business associate agreement. If you are unsure which tool your therapist uses, ask before your first session. For virtual therapy confidentiality, the platform matters as much as the therapist's clinical standards.
